Role-Based Billing Visibility Experiments in Enterprise Accounts
Different roles need different billing data shaped by the decisions they can actually make.
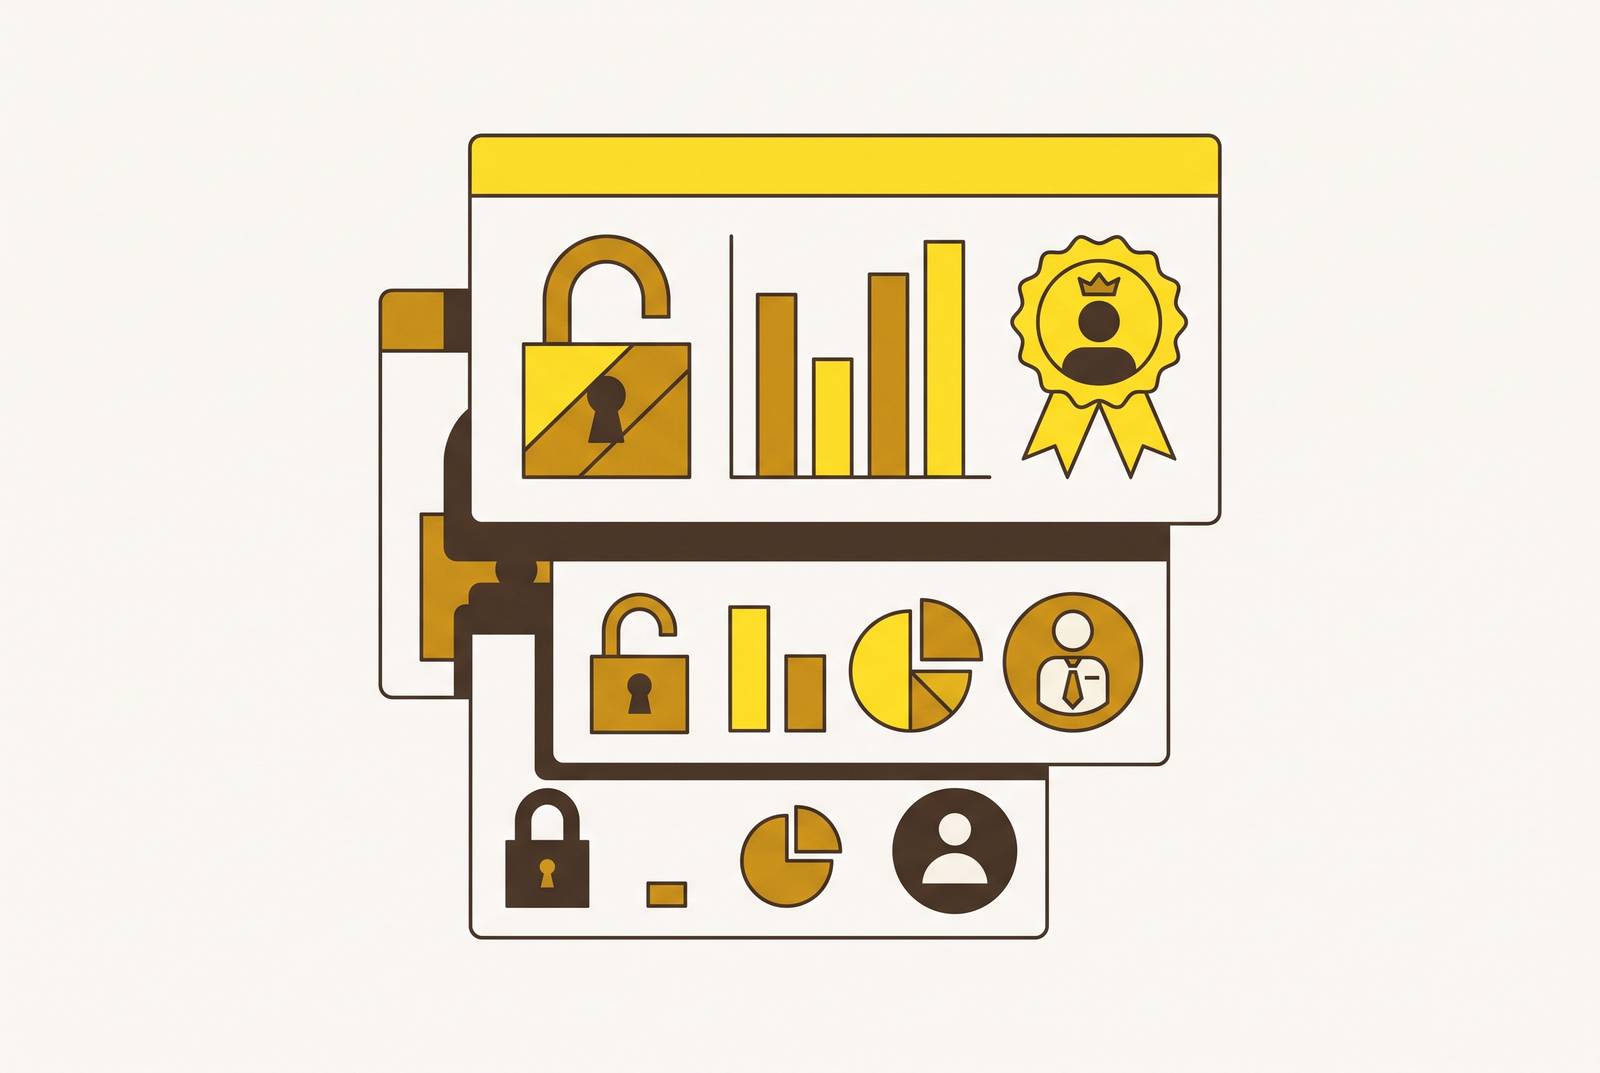
Enterprise billing visibility shapes whether finance, engineering, and department leads can act on usage data without having to ask one another for it. Its design should map what each role sees to the decisions that role can make. As pricing changes, those mappings need to be tested again and again, beyond the one-time permissions setup.
Why enterprise billing visibility is now a product design problem, not just an access control one
A seat-based invoice connects a license to an employee at a flat rate. An invoice for tokens, GPU-minutes, API calls, and workflow executions has no equally simple interpretation. Finance must reconcile the charges, engineering must understand consumption, and department leads must assess the effect on their budgets. Granting everyone access to it does not make it useful to everyone.
That distinction changes the product design task. A single billing view with progressively fewer restrictions assumes that every role needs some portion of the same answer. Usage-based billing instead requires distinct views that surface the signal each role can act on. A consumption rate may matter to the person who can throttle a service, while an attributed invoice total matters to the person approving payment. When the pricing model changes, the signal changes too, so updating the rate card alone cannot keep those views useful.
How decision rights, not org chart position, should determine what each role sees
A department lead authorized to reallocate budget needs current spend by cost center. A developer authorized to throttle API calls needs per-endpoint consumption. A CFO signing invoices needs aggregate reconciliation and audit trails, with no need for raw event logs. These needs differ in scope, detail, and timing, but none follows reliably from seniority.
The error in hierarchy-based design is to treat more data as the natural companion to greater authority. A junior engineer running a cost-sensitive service may need finer, faster data than a VP approving the monthly invoice. Conversely, detailed consumption does not answer whether an invoice reconciles or whether access complied with policy. Visibility should therefore begin with the authorized decision and work backward to the evidence needed to make it. That produces four useful archetypes, namely the enrollment-level administrator, the department administrator, the account owner or engineering lead, and the read-only billing observer.
The four role archetypes that enterprise billing visibility must serve
The enrollment-level administrator is responsible for finance and accounting across the account. Azure's MCA billing roles include billing account owner and reader roles that can see cost and billing data across the account. Azure's EA administrative model gives enterprise administrators access to usage and unbilled charges across accounts, as well as management of reservation and savings plan orders that apply to the Enterprise Agreement. This archetype needs aggregate spend, invoices, price sheets, tax documents, and audit history to support payment approval, reconciliation, and overall budget allocation.
The department administrator has a narrower financial remit. Azure's EA hierarchy places this role below enterprise administrators and above account owners, but charge visibility depends on an explicit policy. This role has decision rights over department budgets, how funds are split across teams, and resource requests. The useful view is therefore department-only spend and usage, with budget-versus-actual tracking and warnings as quotas approach. Peer department charges are not a prerequisite for those decisions.
The account owner or engineering lead controls resource provisioning and responds to consumption anomalies. In Azure's EA model, account owners can see usage for subscriptions they own, while policy controls whether they can see charges. Google Cloud's billing IAM separates account-level from project-level cost viewing. This archetype needs granular consumption for its services, subscriptions, or endpoints.
Azure's Billing Reader role provides subscription billing access without permission to manage or create Azure services. Google Cloud's Billing Account Costs Manager role illustrates a different boundary by allowing budget management and cost viewing and export without pricing configuration access. Because it includes budget management, it is not a strict read-only equivalent. The observer archetype itself needs exportable records, invoice history, and audit logs without write access.
How policy-gated visibility — not just role assignment — gives enterprise administrators fine-grained control
Roles define who is responsible for what, but policies control which data each role can see. In Azure's EA model, this distinction is clear in DA view charges and AO view charges, which enterprise administrators turn on separately. Holding the department administrator or account owner role is necessary but not sufficient for charge visibility. This two-key design lets an organization assign administrative responsibility while keeping charges restricted until its governance framework is ready.
Invoice access exposes another important boundary. Azure's billing access documentation requires a separate invoice-download enablement for MOSP accounts even after Owner, Contributor, Reader, or Billing Reader roles have been assigned. For Microsoft Customer Agreement accounts, those roles grant invoice download directly. The difference illustrates why access to aggregated cost data and access to an invoice document should be treated as separate capabilities. The appropriate gate depends on the account model.
Scope adds a further constraint. Google Cloud's billing IAM supports policies at organization, billing account, and project levels, with higher-level permissions inherited downward. Because permissions are additive, a lower scope cannot block a grant made above it. Effective design requires explicit choices about both role assignment and policy gates, revisited when governance or pricing changes.
Why usage-based and credit-based pricing breaks the assumptions baked into traditional billing visibility design
Traditional subscription visibility rests on costs being predictable, periodic, and attributable to a named user. Usage-based pricing weakens all three assumptions. A department administrator cannot govern an uncertain bill merely by seeing charges after they accrue. The role needs consumption data early enough to act before its budget is exceeded. For AI workloads, a monthly reporting cycle is especially inadequate when a runaway agent can exhaust a department's quarterly budget in hours.
Attribution also becomes more complex than linking a seat to an employee. A workflow executed through a chain of agents can consume inference, retrieval, tool execution, and verification. Each component must be captured and attributed to a cost center. The resulting requirement is not simply a more detailed invoice. Governance needs per-agent cost caps, budget-based circuit breakers, and business-unit allocation, which depend on billing data at the same granularity.
Credit pools partly restore financial predictability by letting departments commit to capacity. However, a remaining balance does not tell a department lead how quickly that capacity is being consumed. Mid-period reallocation requires consumption velocity as well as balance. A system designed around periodic charges must support both financial reporting and signals for intervention during the period.
What billing visibility must actually deliver for each role in a usage-based enterprise account
Finance and accounting leads need aggregate invoice views with cost-center attribution, with no need for raw event logs. Invoice download should be gated separately from dashboard access. Monthly reconciliation should generate automatically rather than occupy the first week of every month with manual work. The view must support payment approval and reconciliation at the level where those decisions occur. More consumption detail is not a substitute for a coherent account of the charges.
Department leads need real-time spend-to-budget ratios scoped to their own cost centers. Alerts must arrive before budget thresholds are reached, while there is still a decision to make. Where the account uses credits, the view must show consumption velocity as well as the remaining balance. The policy layer must enforce the department boundary across its subscriptions or cost centers.
Engineering leads and account owners need near-real-time consumption by service, agent, or endpoint so they can throttle, optimize, or escalate. Multi-agent workflows also require a breakdown by agent role, including orchestrator, retrieval, action, and verification. That breakdown identifies the component driving an overrun without requiring finance to prepare a report. Visibility should remain scoped to the subscriptions or projects the role owns. An account-wide total is too coarse for the intervention engineering is authorized to make.
Compliance and audit observers need read-only exports, role-assignment history, policy-change logs, and invoice history. They should have no write permissions and no way to change role assignments. Their access must also be grantable temporarily without changing the underlying role hierarchy. Across all four archetypes, the test is whether each role can perform its authorized work from its own view. If a department lead must ask engineering to check consumption before approving a request, the visibility design has failed that test.
The infrastructure decisions that make role-appropriate visibility possible at scale
These views depend on dashboard design and the billing system's ability to capture and organize usage. Real-time event ingestion must capture billable activity such as a generated token, a tool call, an agent action, or a retrieval when it happens. Hourly or daily batches cannot support real-time budget alerts or per-request visibility. The latency of the underlying data sets a limit on how quickly any role can respond. A faster interface cannot remove that limit.
The same events must also support aggregation by department, project, agent, and service simultaneously. Running aggregation again each time another role asks for a view does not give all those views at once. Scoped APIs must then expose cost and consumption at the billing account, department, project, or subscription level. This is what allows engineering to retrieve its own data without receiving account-wide access. Google Cloud's separate account-level and project-level cost permissions show how those APIs must limit who can see which costs.
Credit tracking and invoicing impose concurrent requirements on the same engine. An enterprise that uses prepaid capacity still needs its usual invoice data, while department leads need to see credit consumption velocity in real time. Deployment can impose an equally firm constraint. Where usage data cannot legally reside in a vendor's cloud, the infrastructure must run on-premises or in an appropriate sovereign cloud.
An in-house approach requires metering, aggregation, policies, scoped APIs, and dashboards, with continuing work as pricing and governance evolve. A payment-platform metering add-on may shorten the path to an invoice, but its usefulness remains bounded by the pricing dimensions the platform can model. Simultaneous pricing across tokens, GPU-minutes, audio minutes, and hardware tiers is not merely a dashboard configuration task. Unified metering-and-billing infrastructure removes the separate integration project and its reconciliation burden, making visibility architecture and billing architecture part of the same decision.
Treating visibility design as a continuous experiment rather than a one-time configuration
Once the infrastructure supports configurable views, access requires ongoing testing. The choices of granularity, scope, and alert thresholds should be judged by whether they help people make better decisions. Azure's EA policy gates provide a concrete way to extend department or account-owner charge visibility incrementally. Teams should look for earlier budget escalations, fewer requests to finance, and faster responses to anomalies.
The experiments need not always favor more detail. Department leads may benefit from real-time consumption, or they may find that end-of-day summaries support the same decisions with less noise. Cross-team engineering visibility can aid optimization but can also create political friction. Customer-facing dashboards present a similar trade-off, since real-time visibility can reduce bill-shock support tickets while excessive granularity can create confusion. The question in each case is whether the added information improves the action that follows.
Iteration must be possible without an engineering sprint for each visibility change. If changing which roles see which data requires a code deployment, the feedback cycle is too slow to be useful. This matters most when pricing moves from flat-rate to credit-based to outcome-based models, because each transition changes what a role needs to know. Teams that treat billing visibility as a finished permissions project will find themselves rebuilding it whenever their pricing changes.